

CMMC Is Finally Here and the Time to Act is Now
You’ve heard about it for nearly five years. It hit roadblocks, changed leadership, had major revisions, and seemed to stall…but after years of delays and iterations, CMMC is finally signed into law and has an official start date.
The DoD has published the final rule, and beginning on November 10th, 2025 CMMC can be included in any new DoD contract. Keep in mind that it may not appear in all new contracts, but anyone bidding on a contract is expected to have CMMC Level 1 certification in order to do business with the Federal government. Here’s where the really scary news comes in: “only 1% of companies say they’re completely ready to be assessed through the Cybersecurity Maturity Model Certification (CMMC) program, which takes effect on Nov. 10,” according to a report that the managed security provider CyberSheath published on Wednesday October 1st.
For most small businesses this standard has been nothing but a far off threat from the DoD, a “maybe it’ll happen someday”, or, “we’ll cross that bridge when we get to it” type of problem. The issue is that now it is real, it has an official start date, and the DoD base is woefully unprepared. In fact a recent poll showed just how much of the DoD base was underprepared; “16% of respondents reported little to no readiness for CMMC compliance, half admitted to being only moderately or slightly prepared, and 13% said they’d taken no action at all” according to the Redspin CMMC Industry Report.
Quick Refresher on CMMC and How We Got Here:
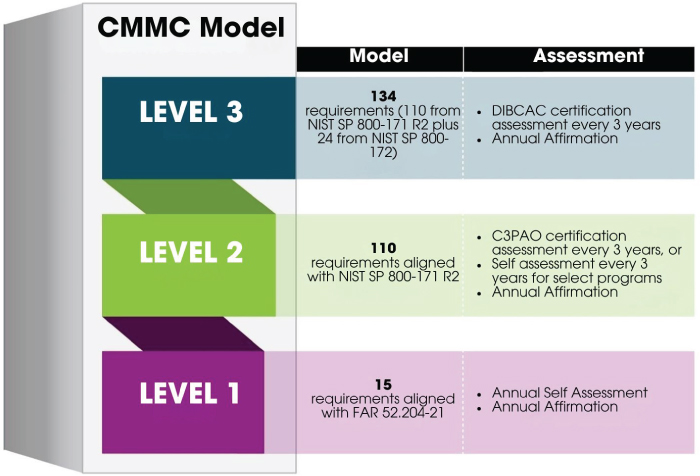
The Cybersecurity Maturity Model Certification (CMMC) announced in 2019 was designed to enhance the security posture of all members of the defense industrial base (DIB). CMMC is an extension of the required security standards introduced in the DFARS (DFARS stands for Defense Federal Acquisition Regulation Supplement. It is a set of regulations that apply to all U.S. Department of Defense (DoD) contracts and subcontracts). DFARS has been in effect for more than 20 years, but enforcement mechanisms and actual implementation have been a consistent problem for the DoD. CMMC is in many ways just DFARS with more enforcement and documentation. CMMC has three levels, Level 1 (Foundational), Level 2 (Advanced), and Level 3 (Expert).
What Should DoD Contractors Be Doing To Get Ready for CMMC?
The first step is accepting that CMMC is real and here to stay, delaying this process any further is a mistake. Next, contractors should focus on what CMMC level they hope to achieve to guide next steps. Once a CMMC level has been determined, a self assessment or assessment utilizing a third party will help determine existing gaps in the current cybersecurity environment. For Level 1 this requires 15 basic security requirements including controlling physical access, utilizing secure passwords, limiting system access to authorized users, etc. Once gaps have been identified they must be corrected and then documented and stored in a System Security Plan (SSP). The last step is either a self assessment or a third party audit by a certified third-party assessor (C3PAO). The result of that assessment must then be uploaded to the SPRS (Supplier Performance Risk System), and updated annually. Keep in mind that currently there are a limited number of C3PAOs and companies authorized to support CMMC implementation and assessment. With a limited number of assessors, and a large number of contractors needing CMMC support there is a real possibility of delays and overwhelming demand. CMMC implementation is different for every company, and is impacted by size and complexity of the organization as well as current cybersecurity readiness and documentation.
Want to learn more about CMMC? Attend IES’s free webinar on Thursday October 9th to hear more about CMMC and what it means for DoD contractors.

Resources for CMMC:
